Building the Trust Layer: Escrow, Verification, and Dispute Resolution in Fintech Marketplaces
In any platform where money moves between strangers, trust is not a brand attribute. It is an engineering deliverable. The trust layer is the set of mechanisms that make a participant willing to send funds to someone they have never met, and it is usually the difference between a marketplace that captures its transactions and one that watches them happen over WhatsApp.
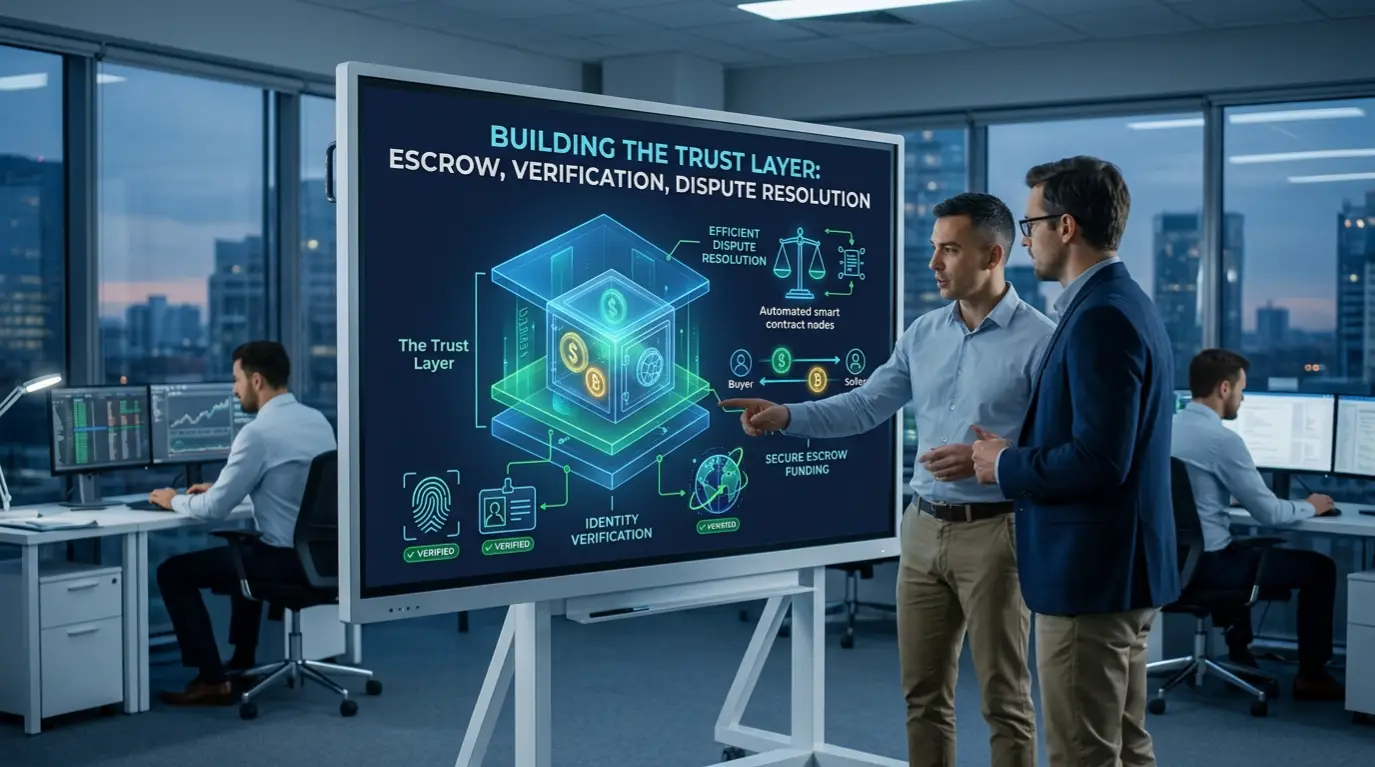
This article breaks the trust layer into its component parts and describes the design decisions that matter most in each.
Identity and Verification: Proportional, Not Maximal
Verification exists to answer one question: how confident is the platform that this participant is who they claim to be and can be held accountable? The temptation is to demand maximum documentation from everyone at signup. This reliably destroys conversion.
A better model is progressive verification tied to risk exposure. A new user browsing requires nothing. A user listing an item requires an email and phone. A user receiving a payout requires identity documents and bank verification. A user transacting above a threshold triggers enhanced due diligence. Each step is requested at the moment its value is obvious to the user, which is when they are about to receive money.
Practical considerations:
- Store verification state, not documents, wherever the provider allows it. Holding identity documents creates a liability that most early-stage platforms are not equipped to manage.
- Design for re-verification. Documents expire, businesses change ownership, and regulations shift. A verification model that assumes a one-time event will require rework.
- Make the failure path humane. A rejected verification with no explanation is the single most common cause of high-value supply abandoning a platform permanently.
Escrow and Fund Flow: Where the Money Actually Sits
The core design question is when the platform takes control of funds and when it releases them. Three common patterns:
Direct pass-through. The buyer pays the seller, the platform takes a fee. Simple, minimal regulatory exposure, but the platform has almost no leverage in a dispute and a weak claim to a meaningful take rate.
Delayed capture. The buyer’s payment method is authorized at booking and captured at fulfilment. Low complexity, works well for services with short lead times, but authorization windows expire and the pattern breaks down for long-cycle transactions.
True escrow. Funds are captured at purchase, held in a segregated account, and released on a defined trigger — delivery confirmation, elapsed time, milestone approval, or dispute resolution. This gives the platform real leverage and justifies a higher take rate, but it carries licensing implications in most jurisdictions and typically requires working with a regulated partner rather than holding funds directly.
The mistake to avoid is designing the product experience first and discovering the fund-flow constraints afterwards. Release triggers, refund windows, and partial-refund logic ripple into the UI, the notification system, the accounting model, and the support workflow. Teams that build multi-sided payment systems regularly — the group at u1core.com among them — usually map the money flow before the first screen is designed, because reversing that order means rebuilding both.
Split Payments and Multi-Party Settlement
Once more than two parties share a transaction — platform fee, seller payout, affiliate commission, tax withholding, insurance premium — settlement becomes a ledger problem rather than a payments problem.
Two rules save considerable pain later. First, record intent and outcome separately: what the system decided each party should receive, and what each party actually received, with the gap explicitly reconciled. Second, make every monetary movement an immutable ledger entry rather than a mutable balance field. Balances derived from an append-only ledger can be audited; balances updated in place cannot, and finance teams will eventually need the audit.
Dispute Resolution as a Product Surface
Most platforms treat disputes as a support ticket queue. This works until volume grows, at which point resolution times climb, both sides lose confidence, and chargebacks rise.
A well-designed dispute system has four properties:
- Structured intake. The claimant selects a category and provides category-specific evidence, rather than writing a paragraph. Structured claims can be routed, measured, and eventually partially automated.
- Defined timelines. Each party has a fixed window to respond, with automatic resolution if they do not. Ambiguous timelines produce indefinite holds on funds, which is the outcome both sides hate most.
- Published policy. Participants should be able to read, before transacting, what happens if the transaction goes wrong. Unpublished discretionary policy is perceived as arbitrary even when it is applied fairly.
- Outcome data feeding back into risk. Repeated disputes against a seller should affect their verification tier, payout timing, or listing visibility automatically.
Reputation Systems That Resist Gaming
Ratings are the cheapest trust signal and the easiest to manipulate. A few design choices materially improve signal quality:
- Only allow reviews from verified completed transactions.
- Reveal both parties’ reviews simultaneously after both are submitted, or after the window closes, to prevent retaliatory rating.
- Weight recent transactions more heavily than old ones, so reputation reflects current behaviour.
- Display volume alongside score, since a perfect rating from three transactions means little.
- Surface objective signals — response time, completion rate, dispute rate — alongside subjective stars.
Fraud Controls Without Killing Conversion
Fraud prevention is a balance between false positives, which cost revenue and goodwill, and false negatives, which cost money directly. The most effective early-stage approach is layered: cheap deterministic rules catch obvious cases, a risk score routes the ambiguous middle to review, and only genuinely high-risk transactions face hard blocks. Critically, every automated decision should be logged with its inputs, so that the team can measure the false-positive rate rather than guessing at it.
Sequencing the Build
Not all of this is needed at launch. A reasonable order for most platforms is: basic identity verification and a clear refund policy first; escrow or delayed capture as soon as transaction values justify it; structured disputes when manual handling exceeds a few hours per week; automated risk scoring when fraud losses become measurable; and sophisticated reputation weighting once transaction volume makes the data meaningful.
What should not be deferred is the underlying data model. Ledger structure, verification state, and dispute records are extremely difficult to retrofit onto a system that was not designed for them. The interface can evolve; the foundation should be right from the start.